Security
you can see.
From a single 0–100 exposure score to attack-path exposure, here's Mantis360 turning raw scan data into a decision you can act on.
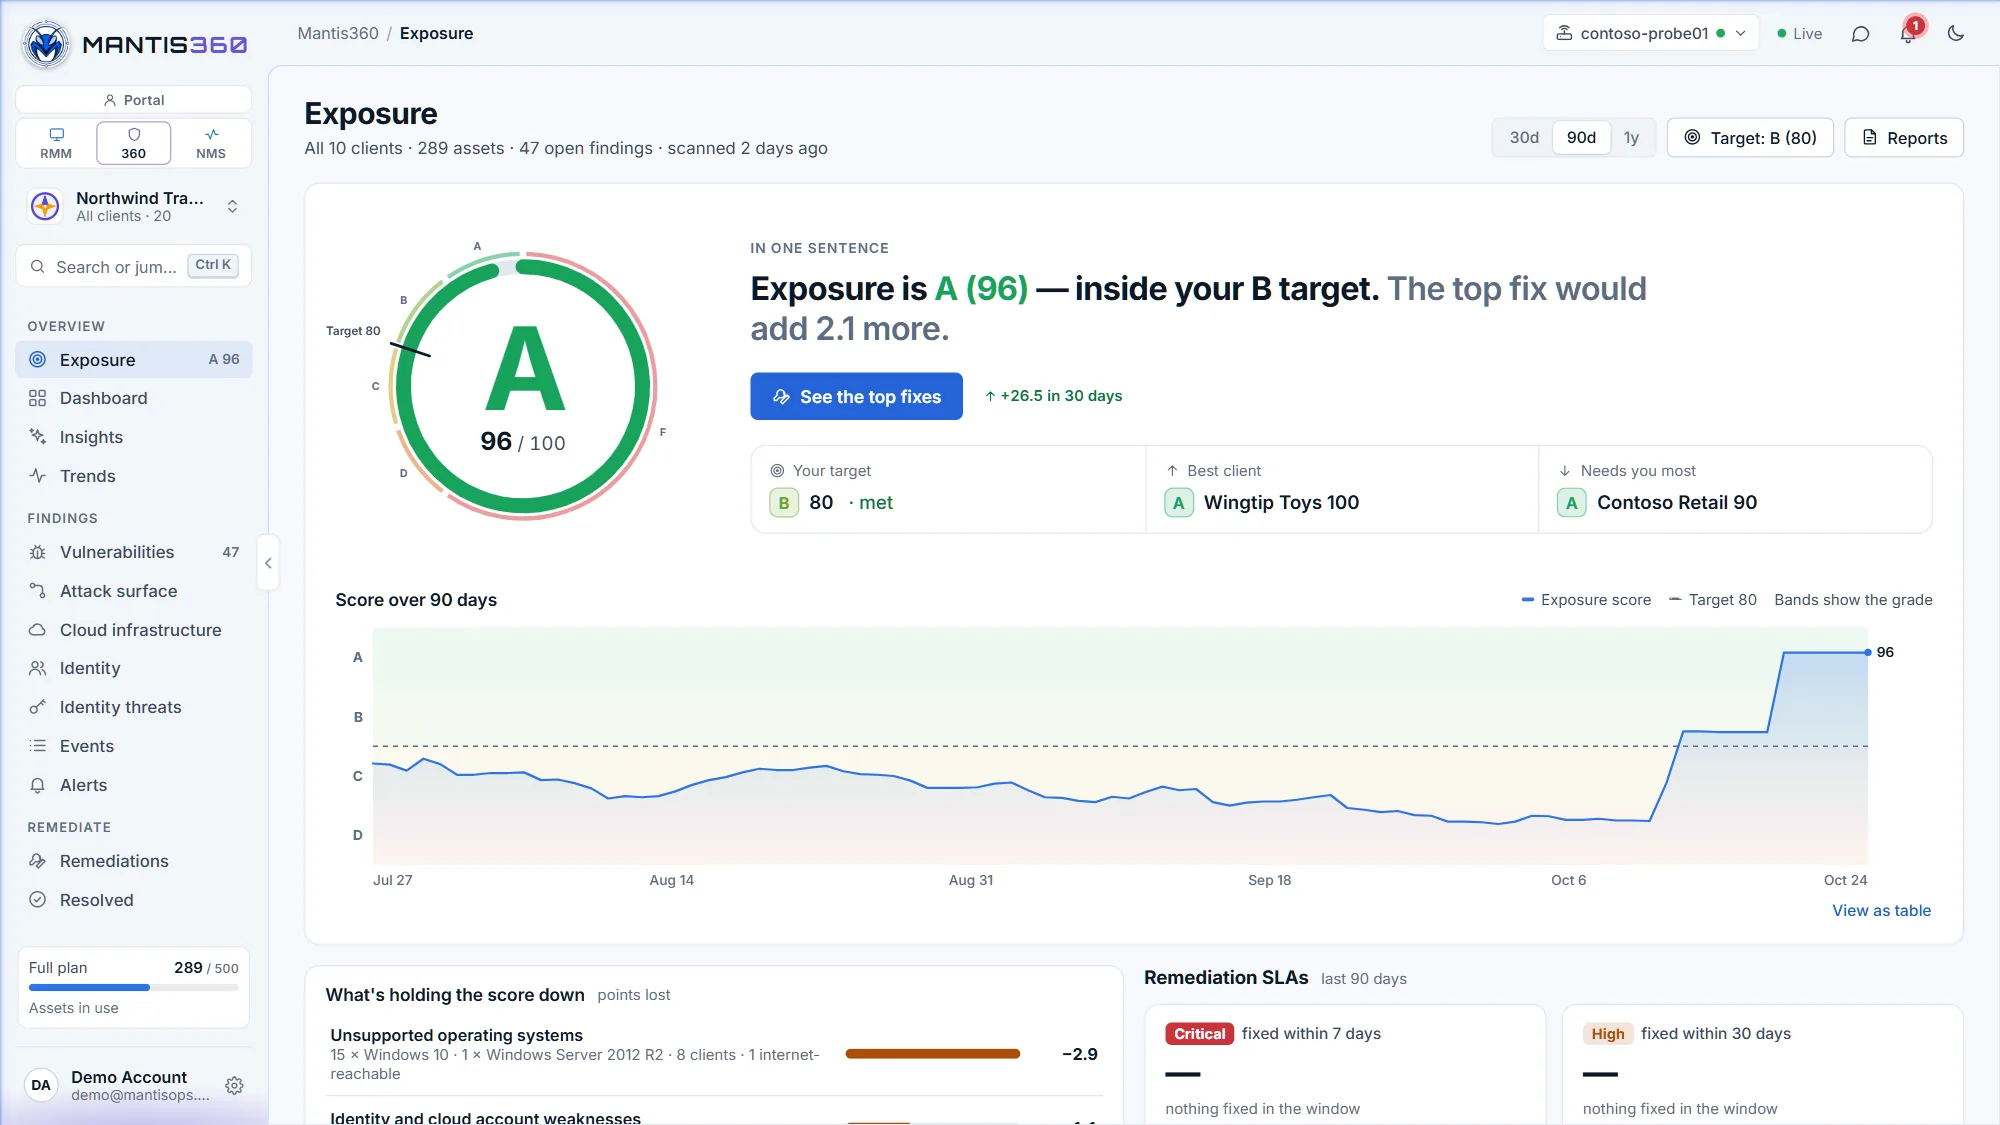
Security posture, quantified
One 0–100 exposure score with an A–F grade, the 90-day trend behind it, the drivers holding it down, and your best and worst client side by side.
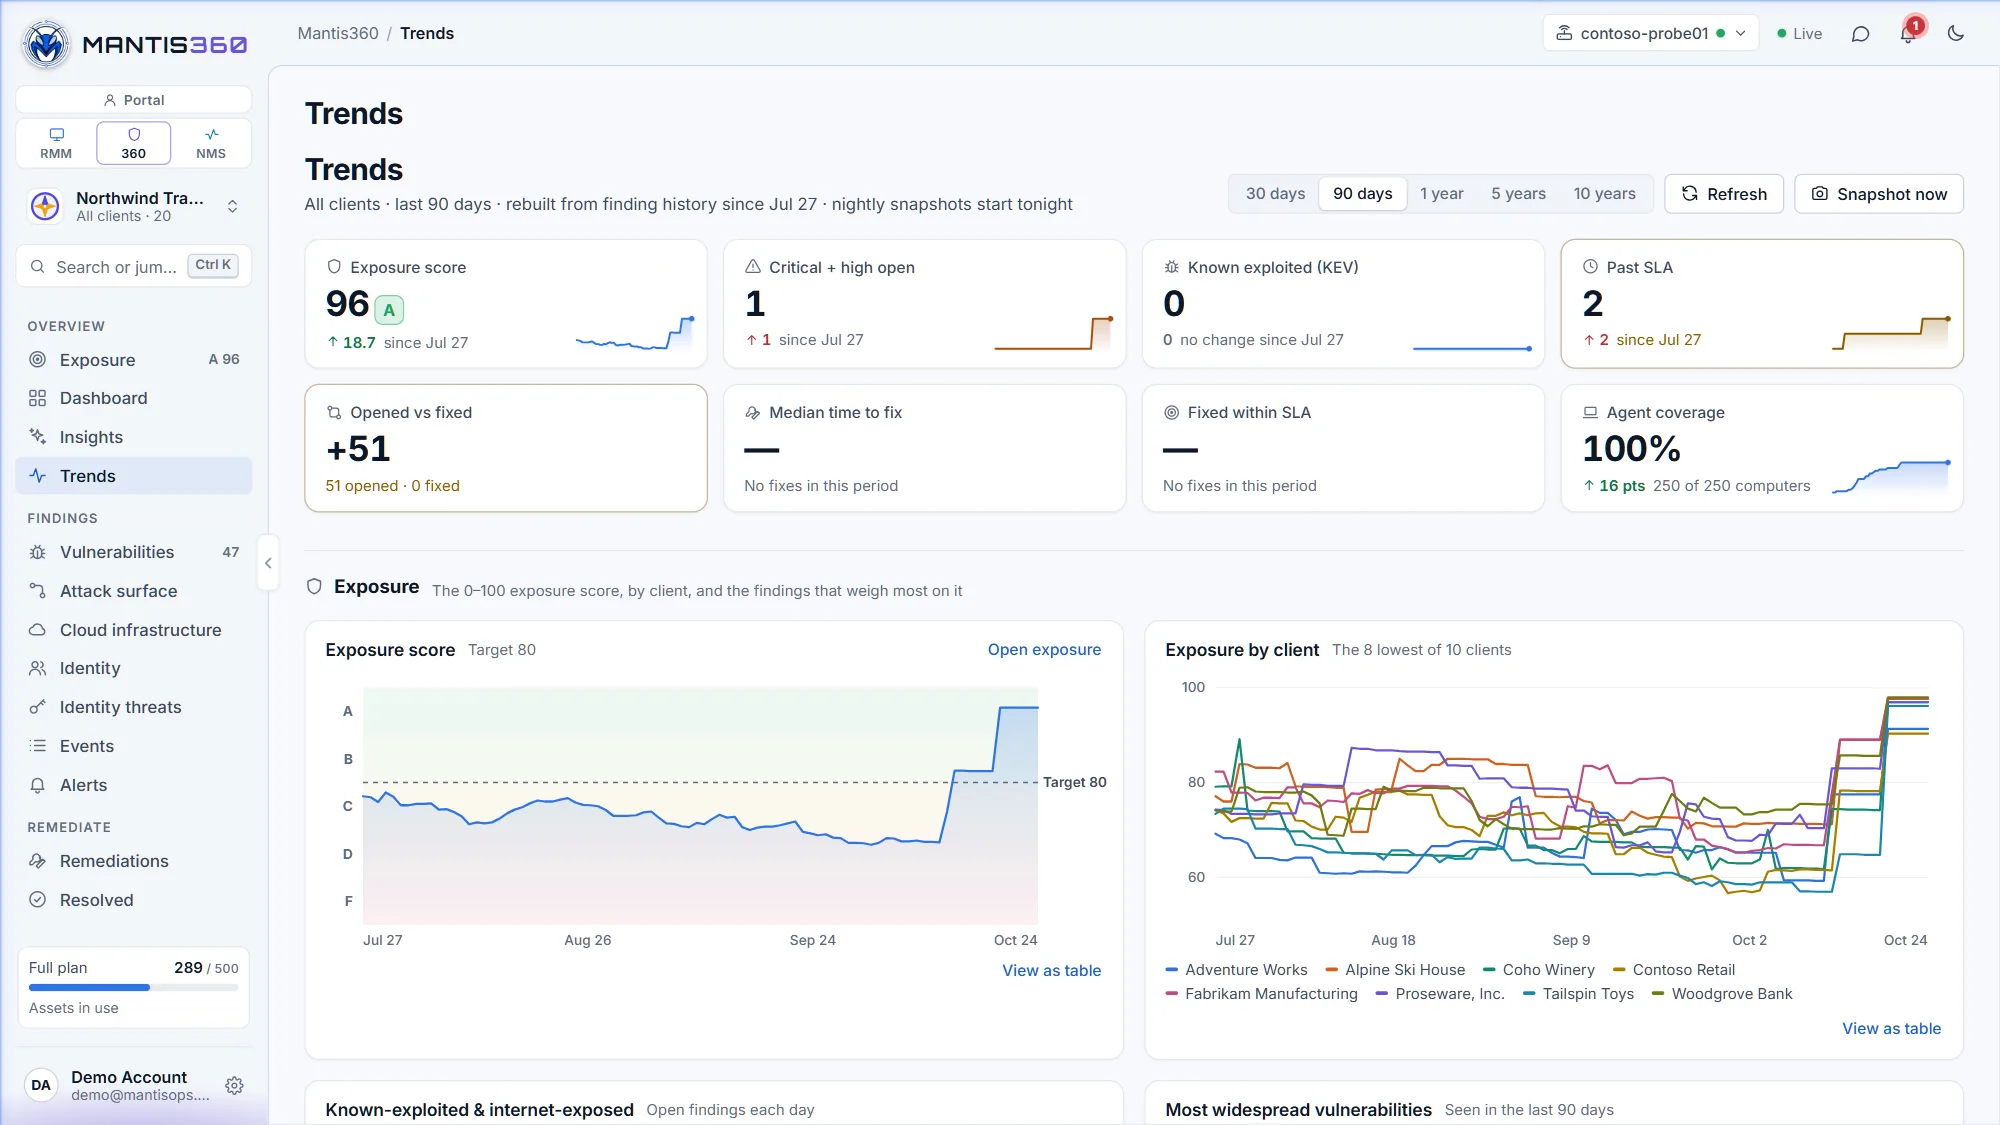
Trends you can show a client
Exposure score, critical and known-exploited findings, SLA, opened vs fixed and agent coverage over 30 days to 10 years — for every client or just one.
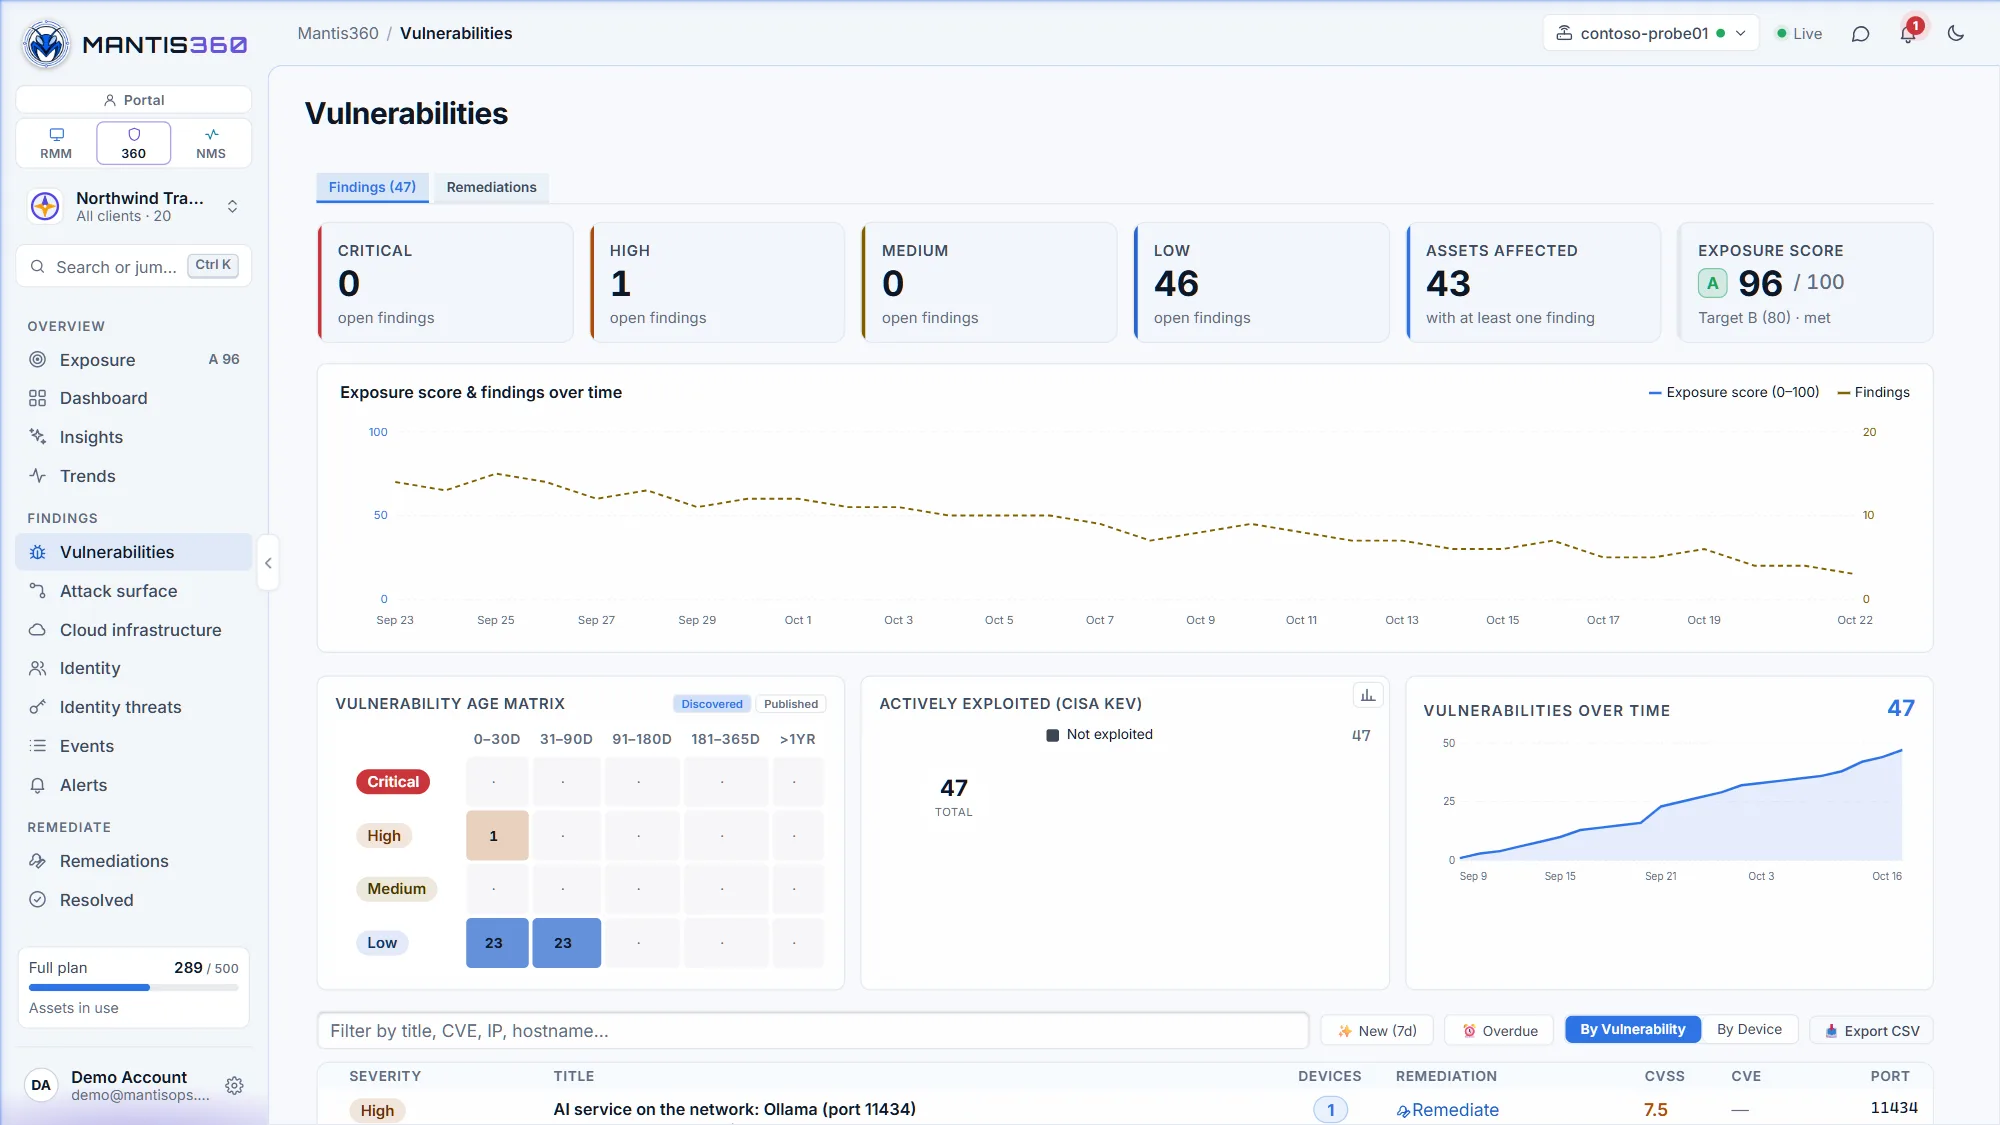
Findings that prioritize themselves
CVSS, EPSS and CISA KEV correlated into one ranked list — Log4Shell, Zerologon, EternalBlue and the rest, with SLA tracking built in.
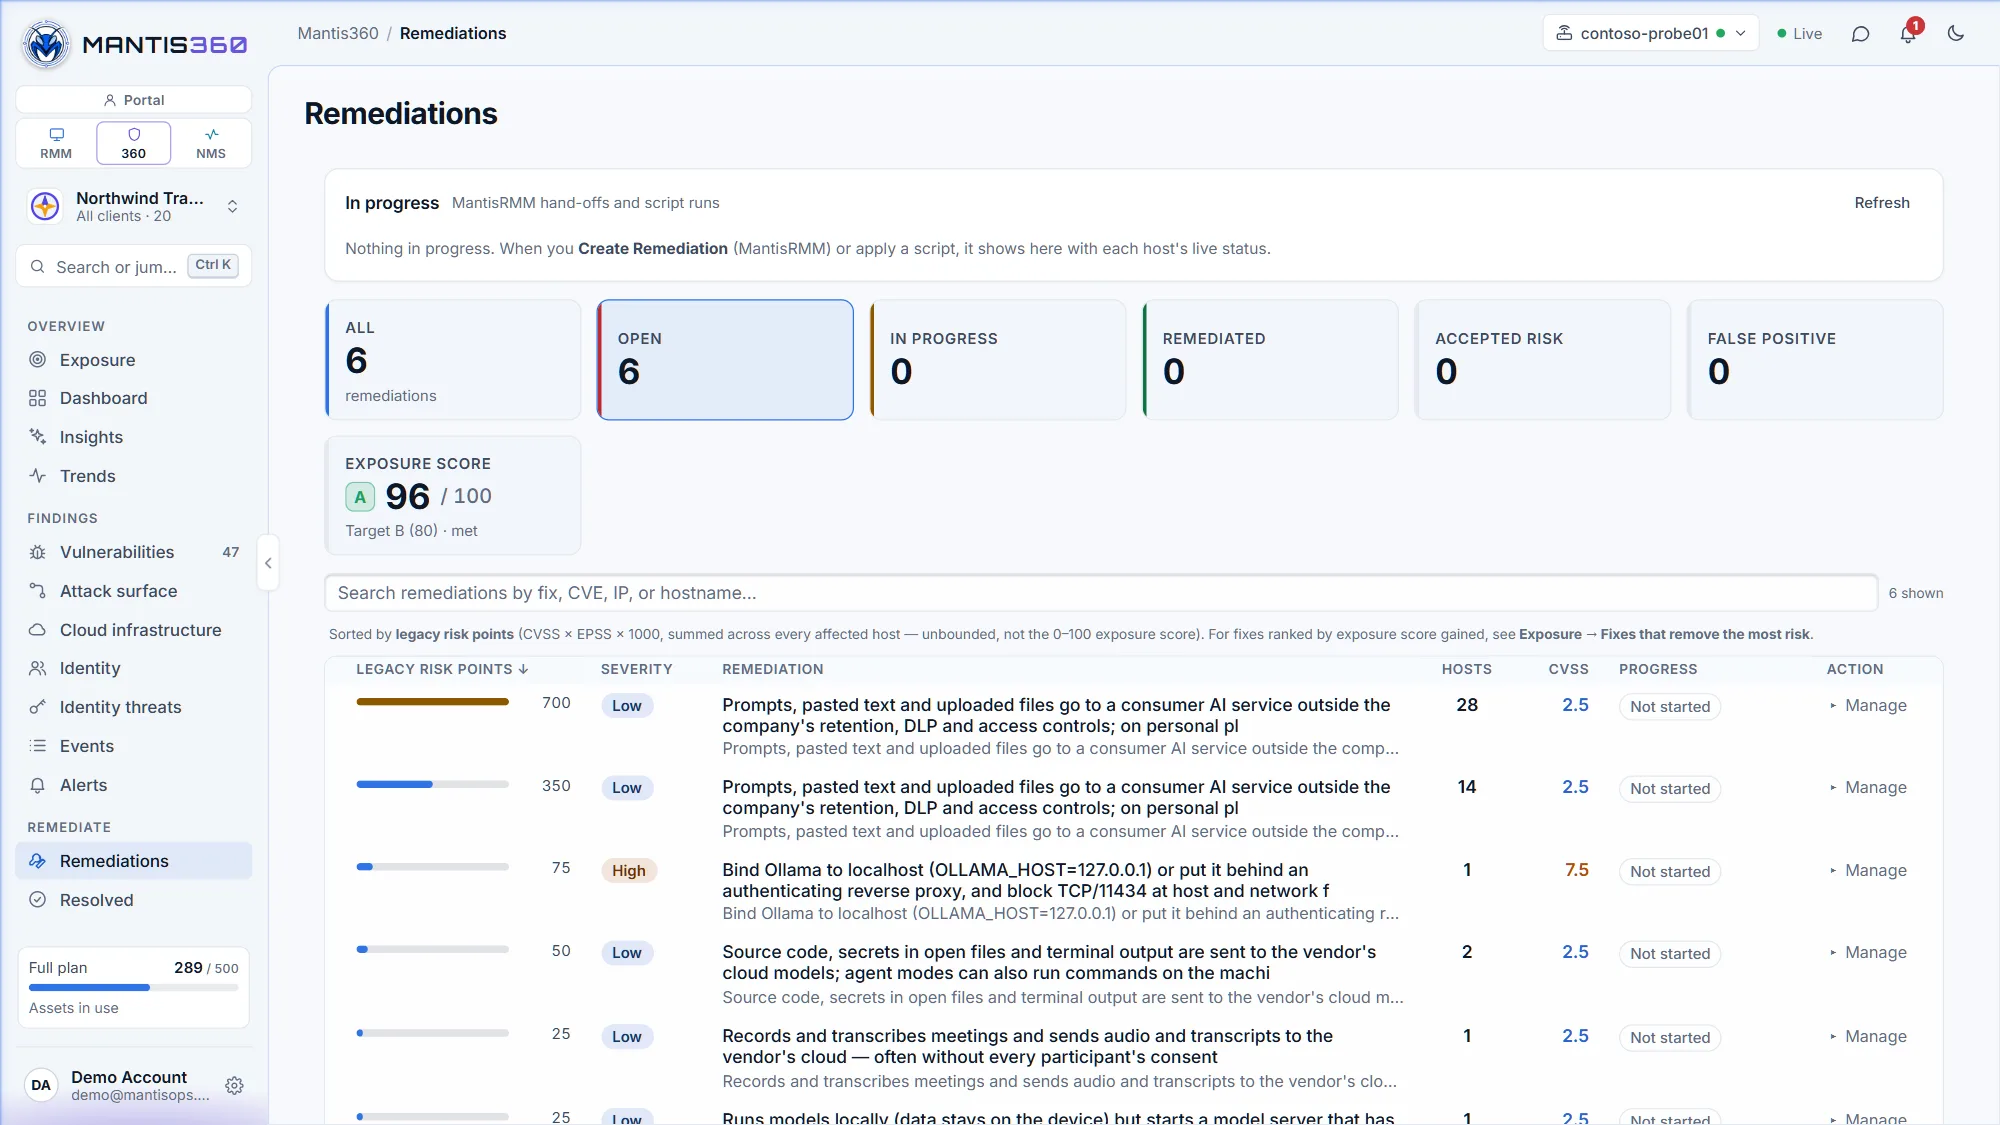
From finding to fixed
Findings grouped into the fixes that close them and ranked by risk impact — track open, in-progress, accepted, and remediated work across every client.
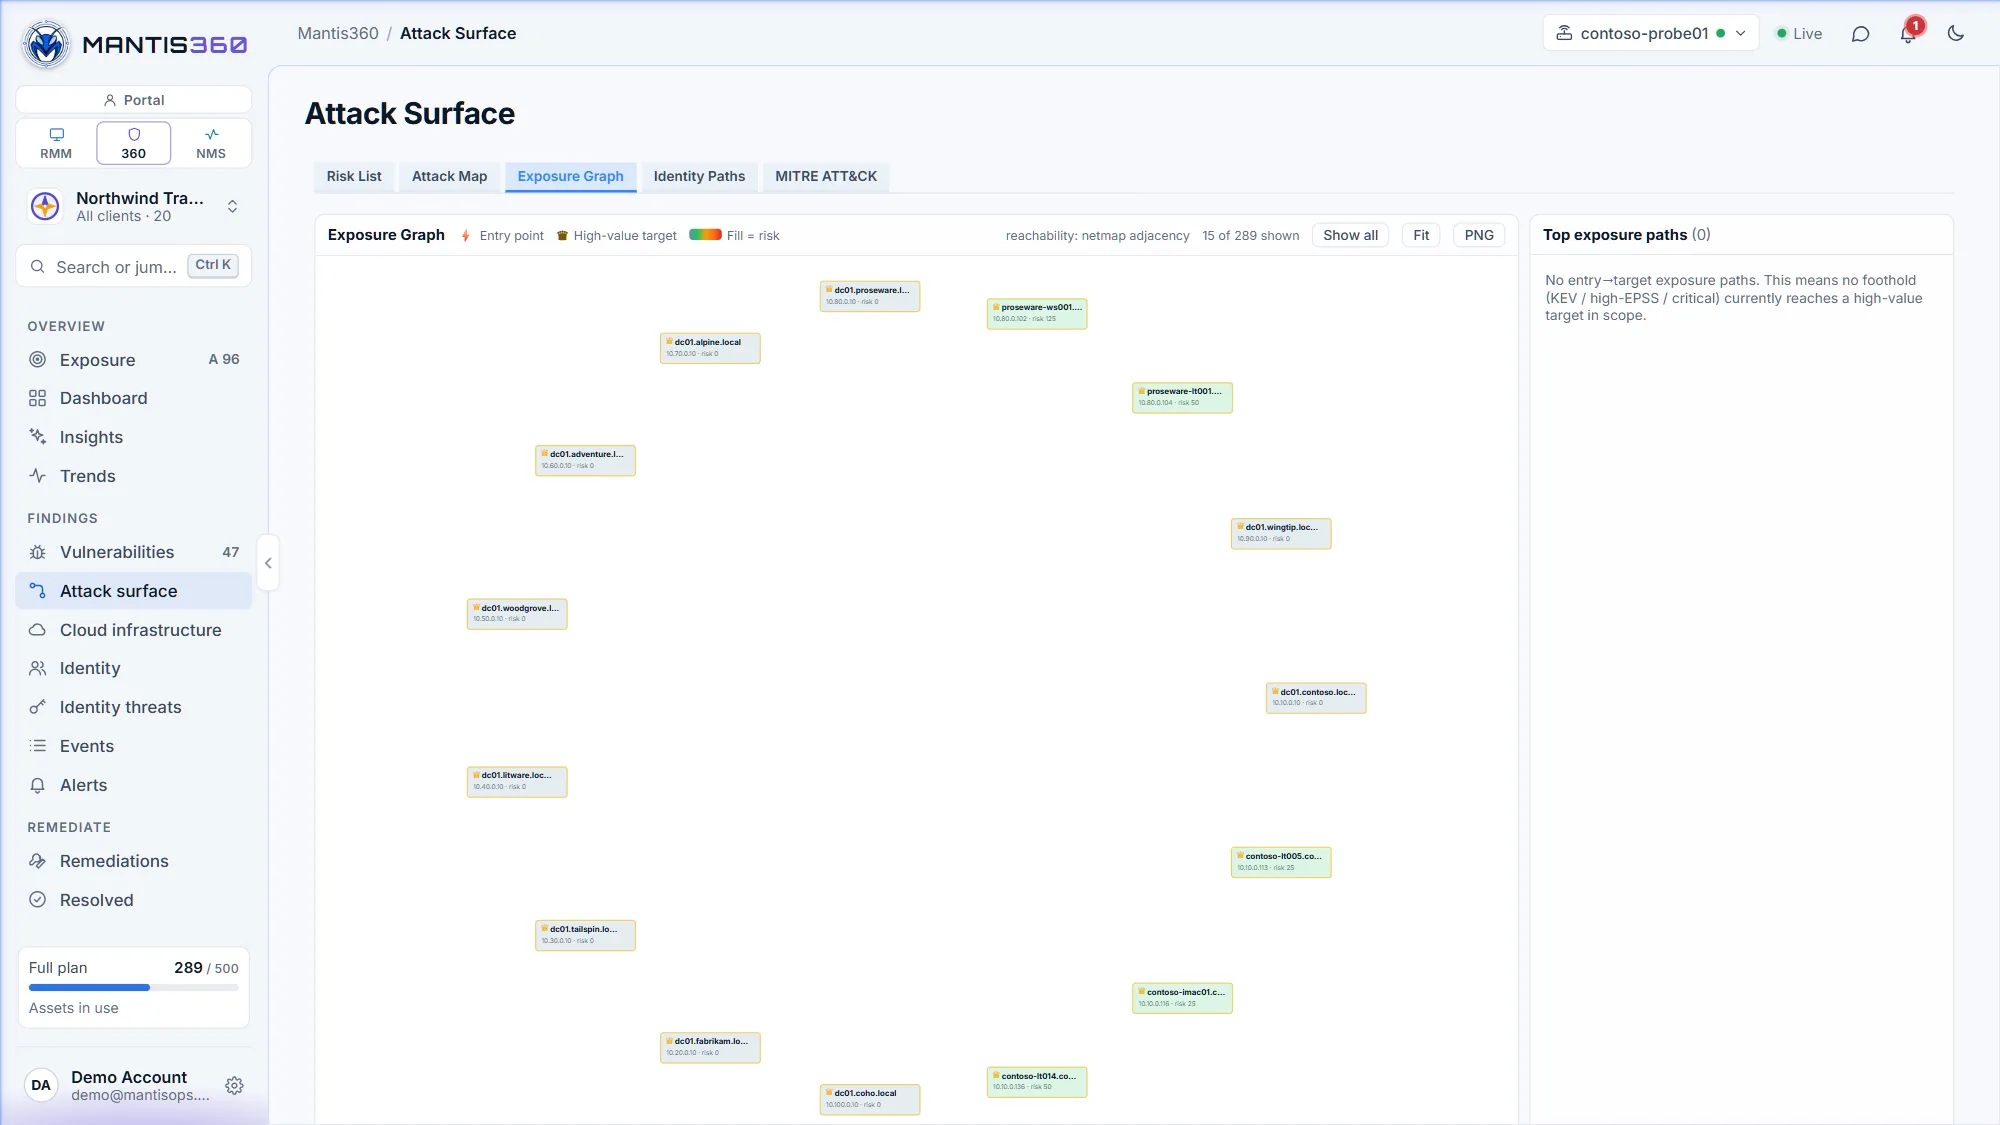
See the blast radius
The exposure graph maps how an exploited foothold reaches your domain controllers and high-value targets.
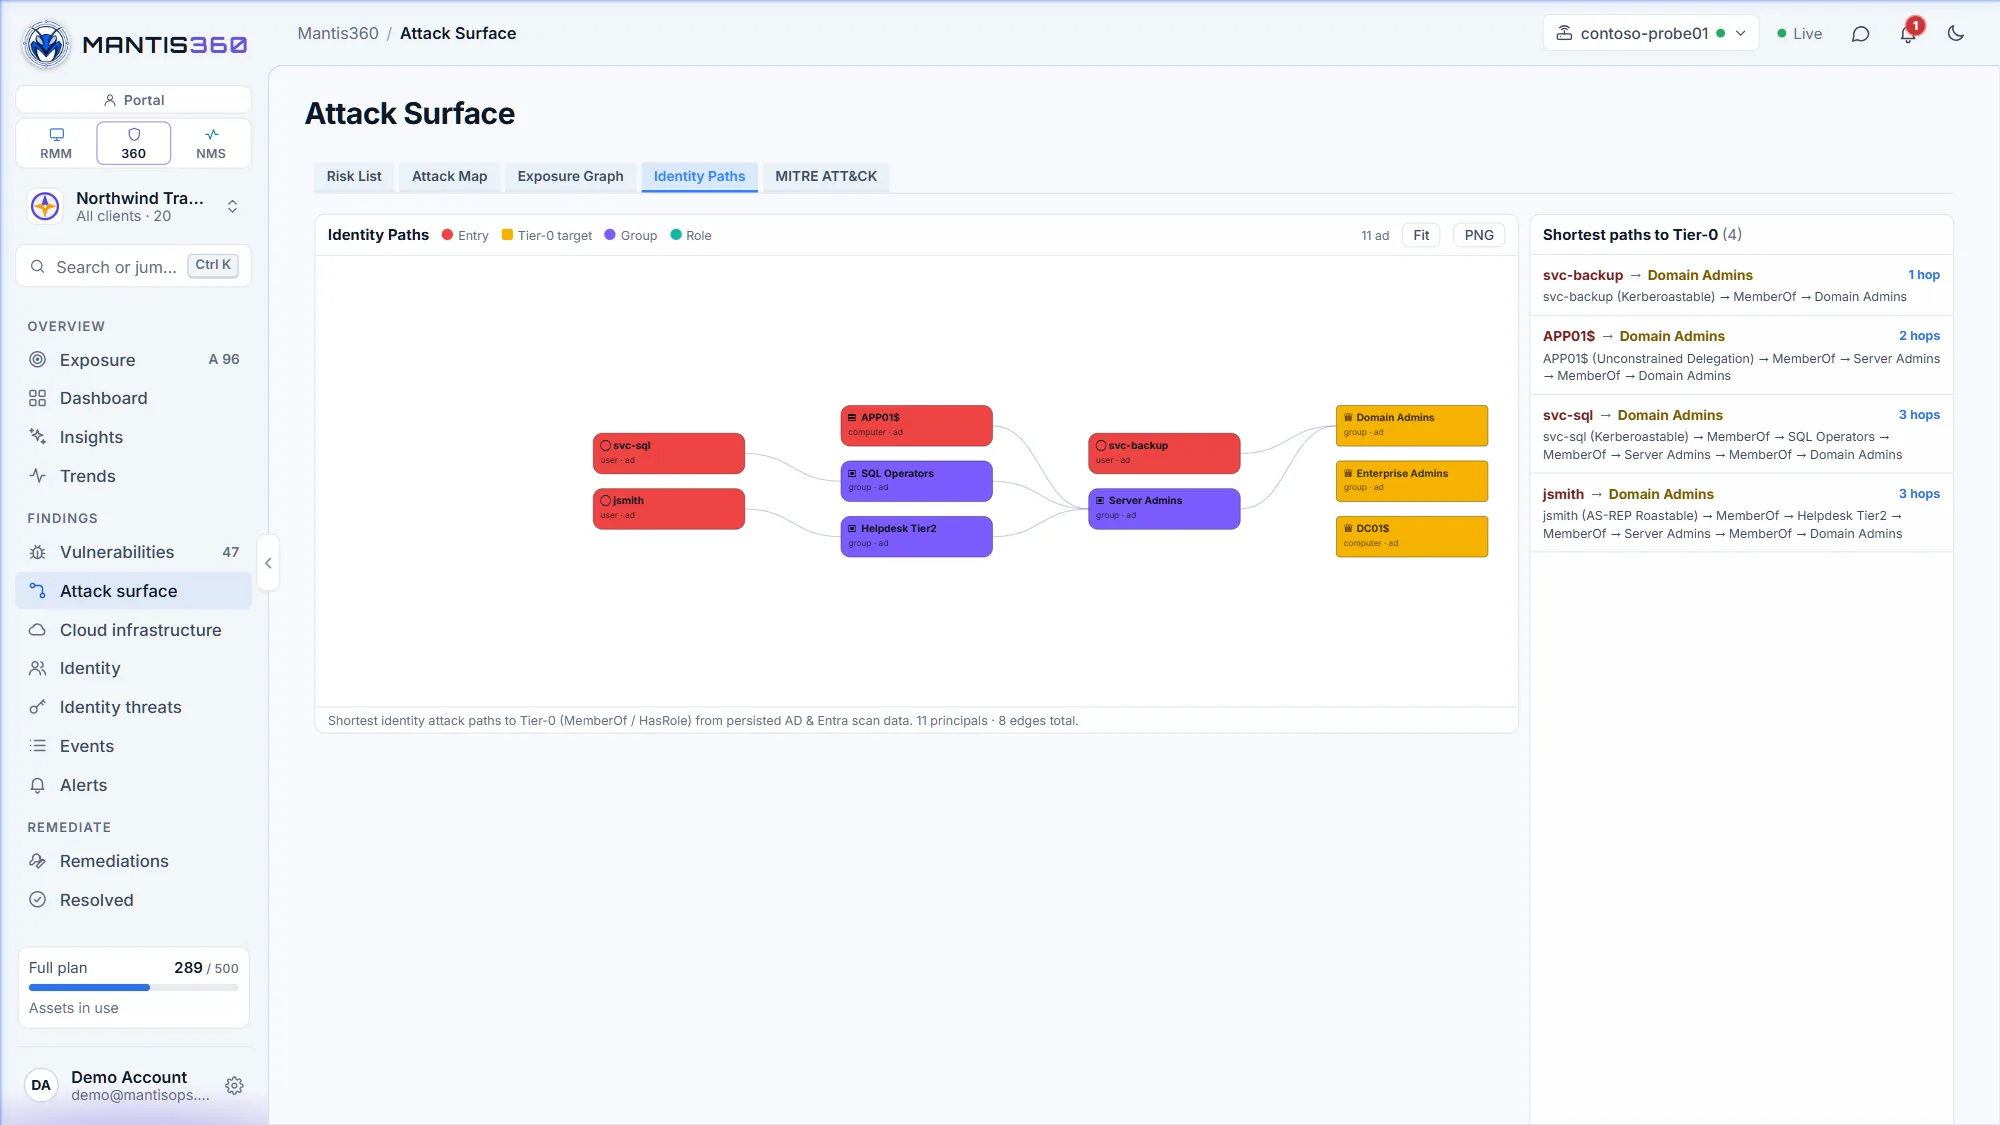
Identity attack paths
Kerberoastable service accounts, AS-REP roastable users, and nested groups traced all the way to Domain Admins.
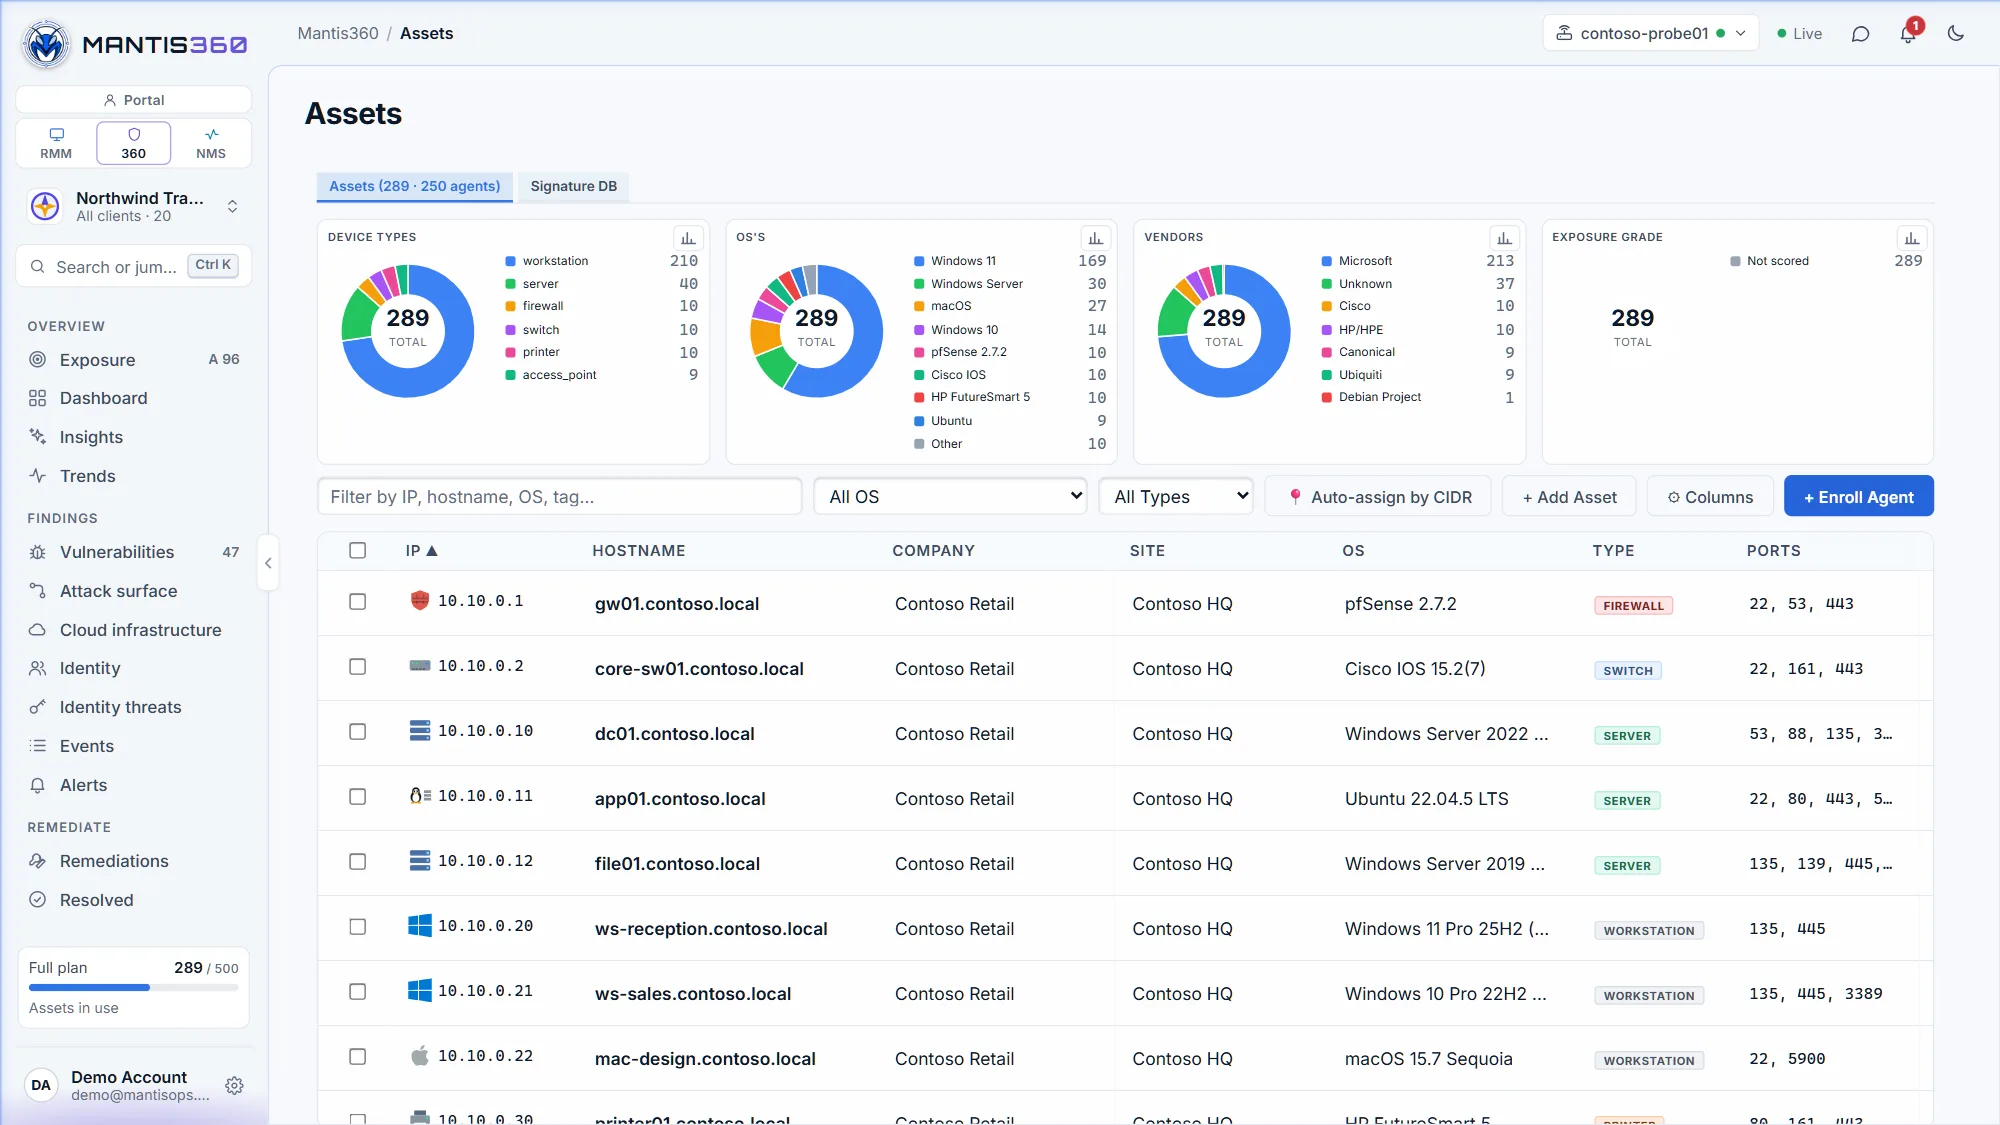
Every asset, discovered and classified
Servers, workstations, firewalls, switches, printers, and access points — fingerprinted and broken down by type and OS across every site.
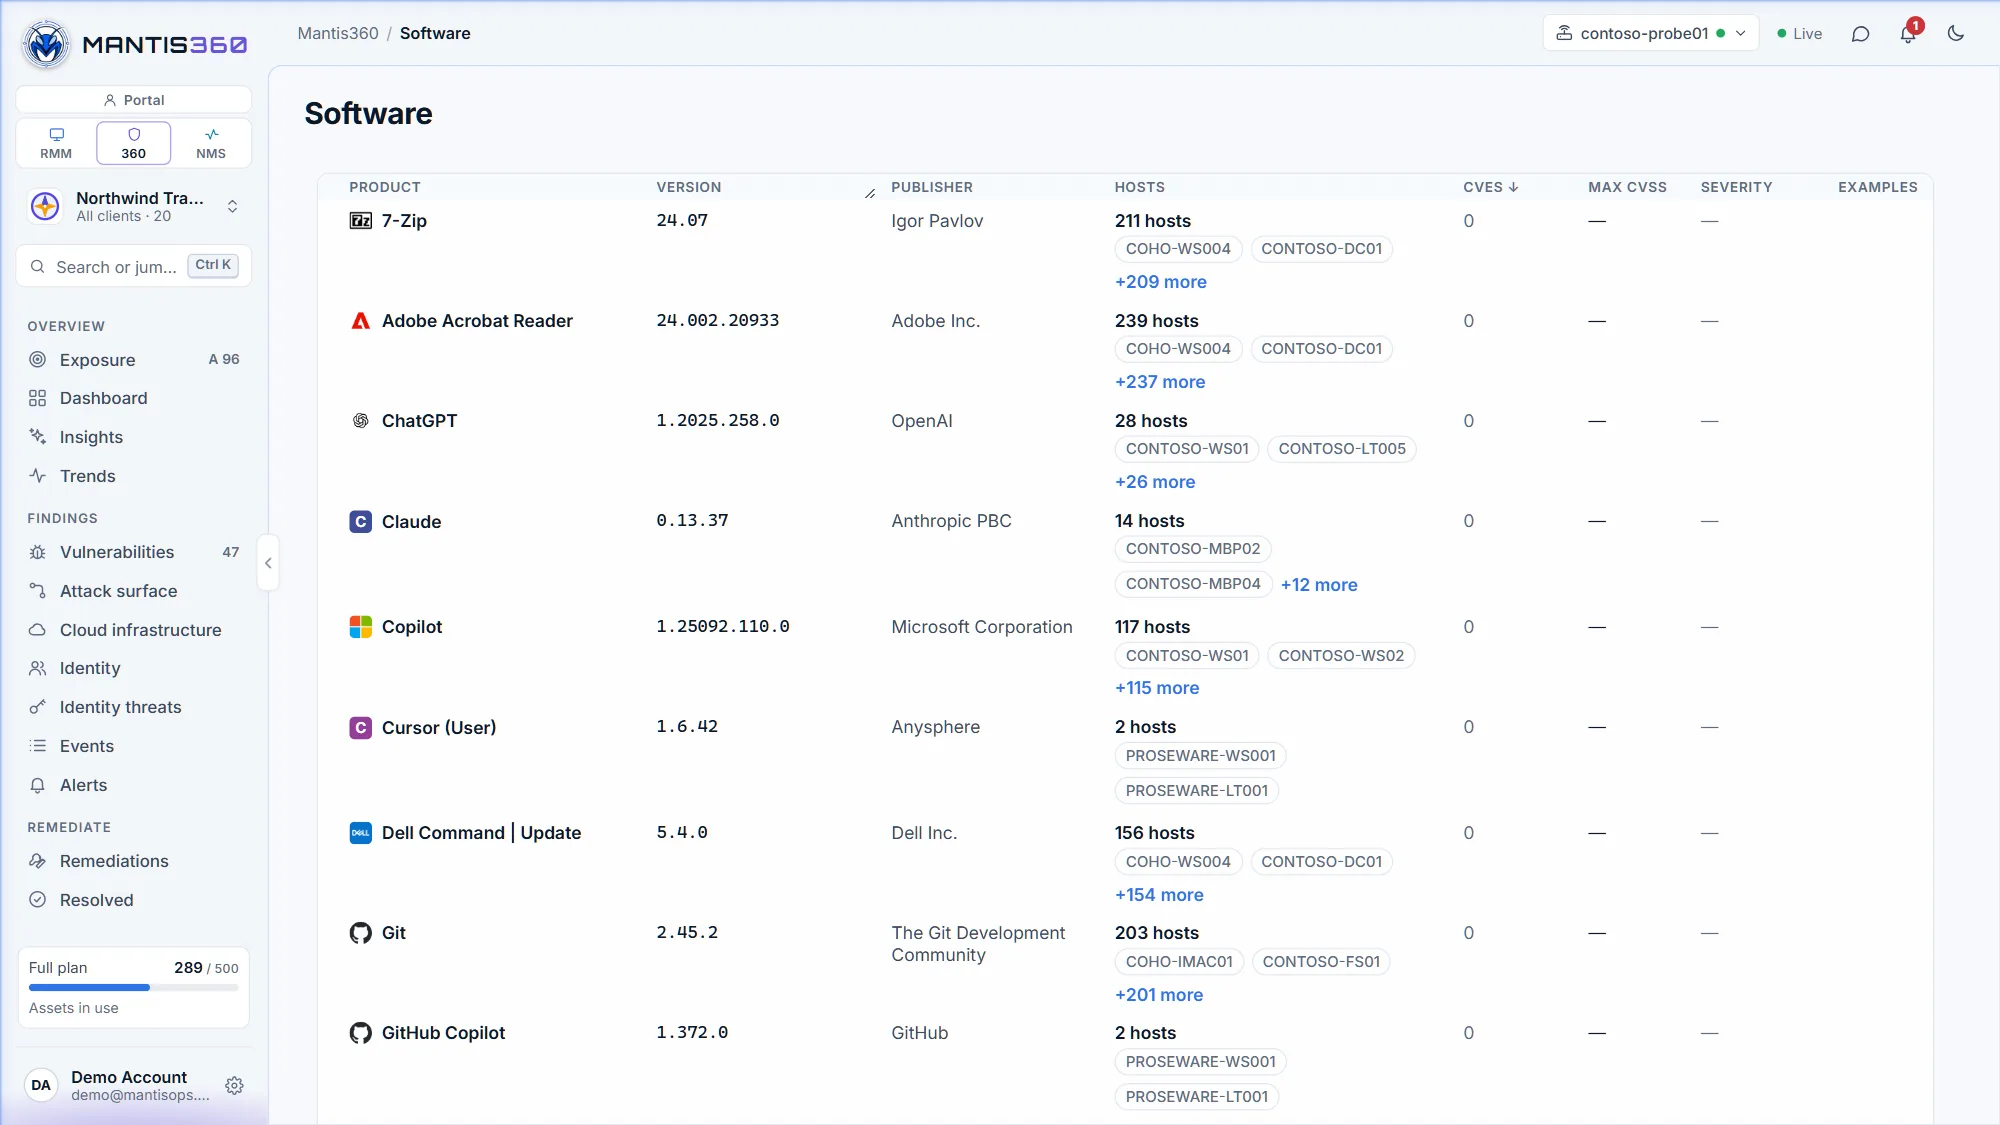
Vulnerable software, found on the endpoint
Installed software across every endpoint, matched against known CVEs — so you know which Chrome, 7-Zip or WinRAR to update first.
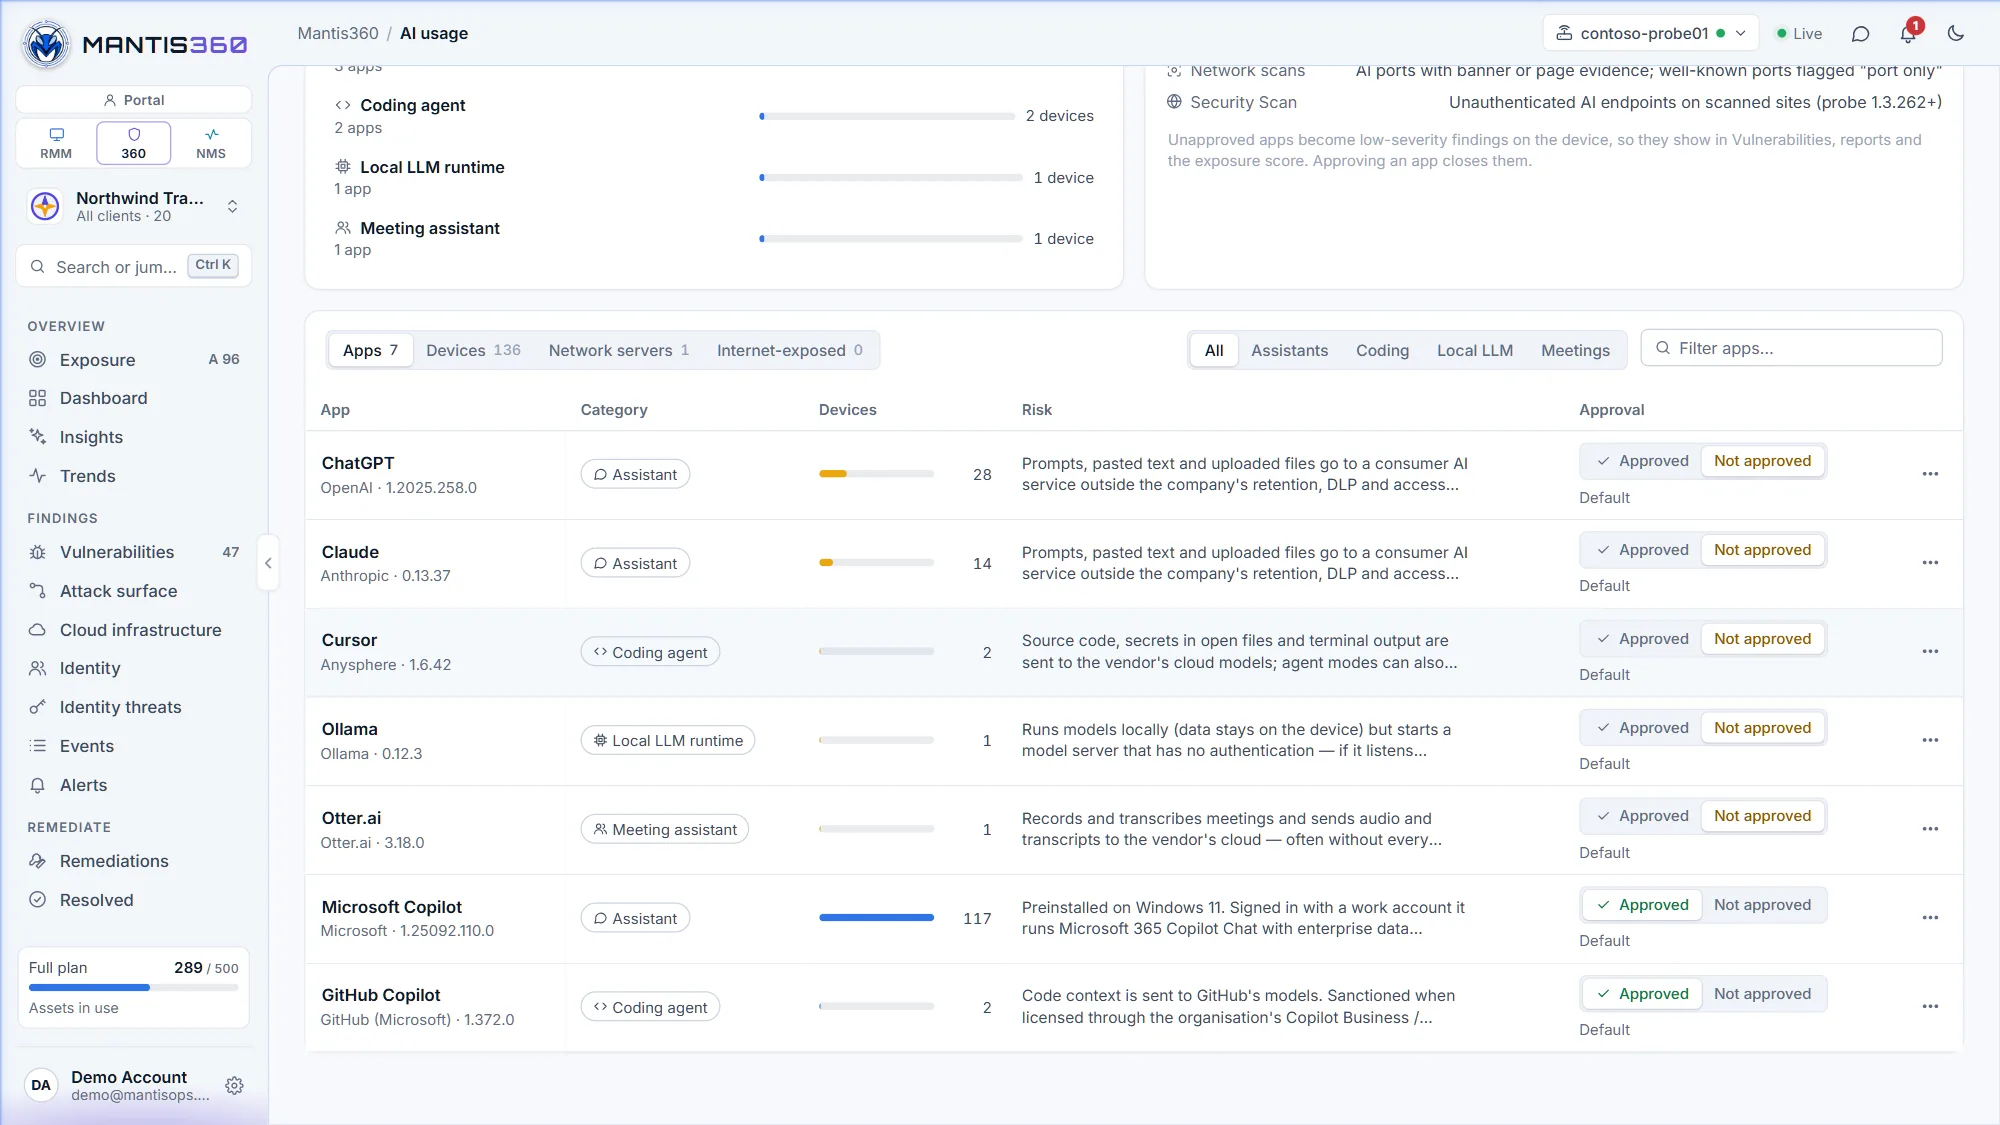
Shadow AI, app by app
Every AI app found in software inventory, with its category, the devices running it, why it's a risk and whether you've approved it.
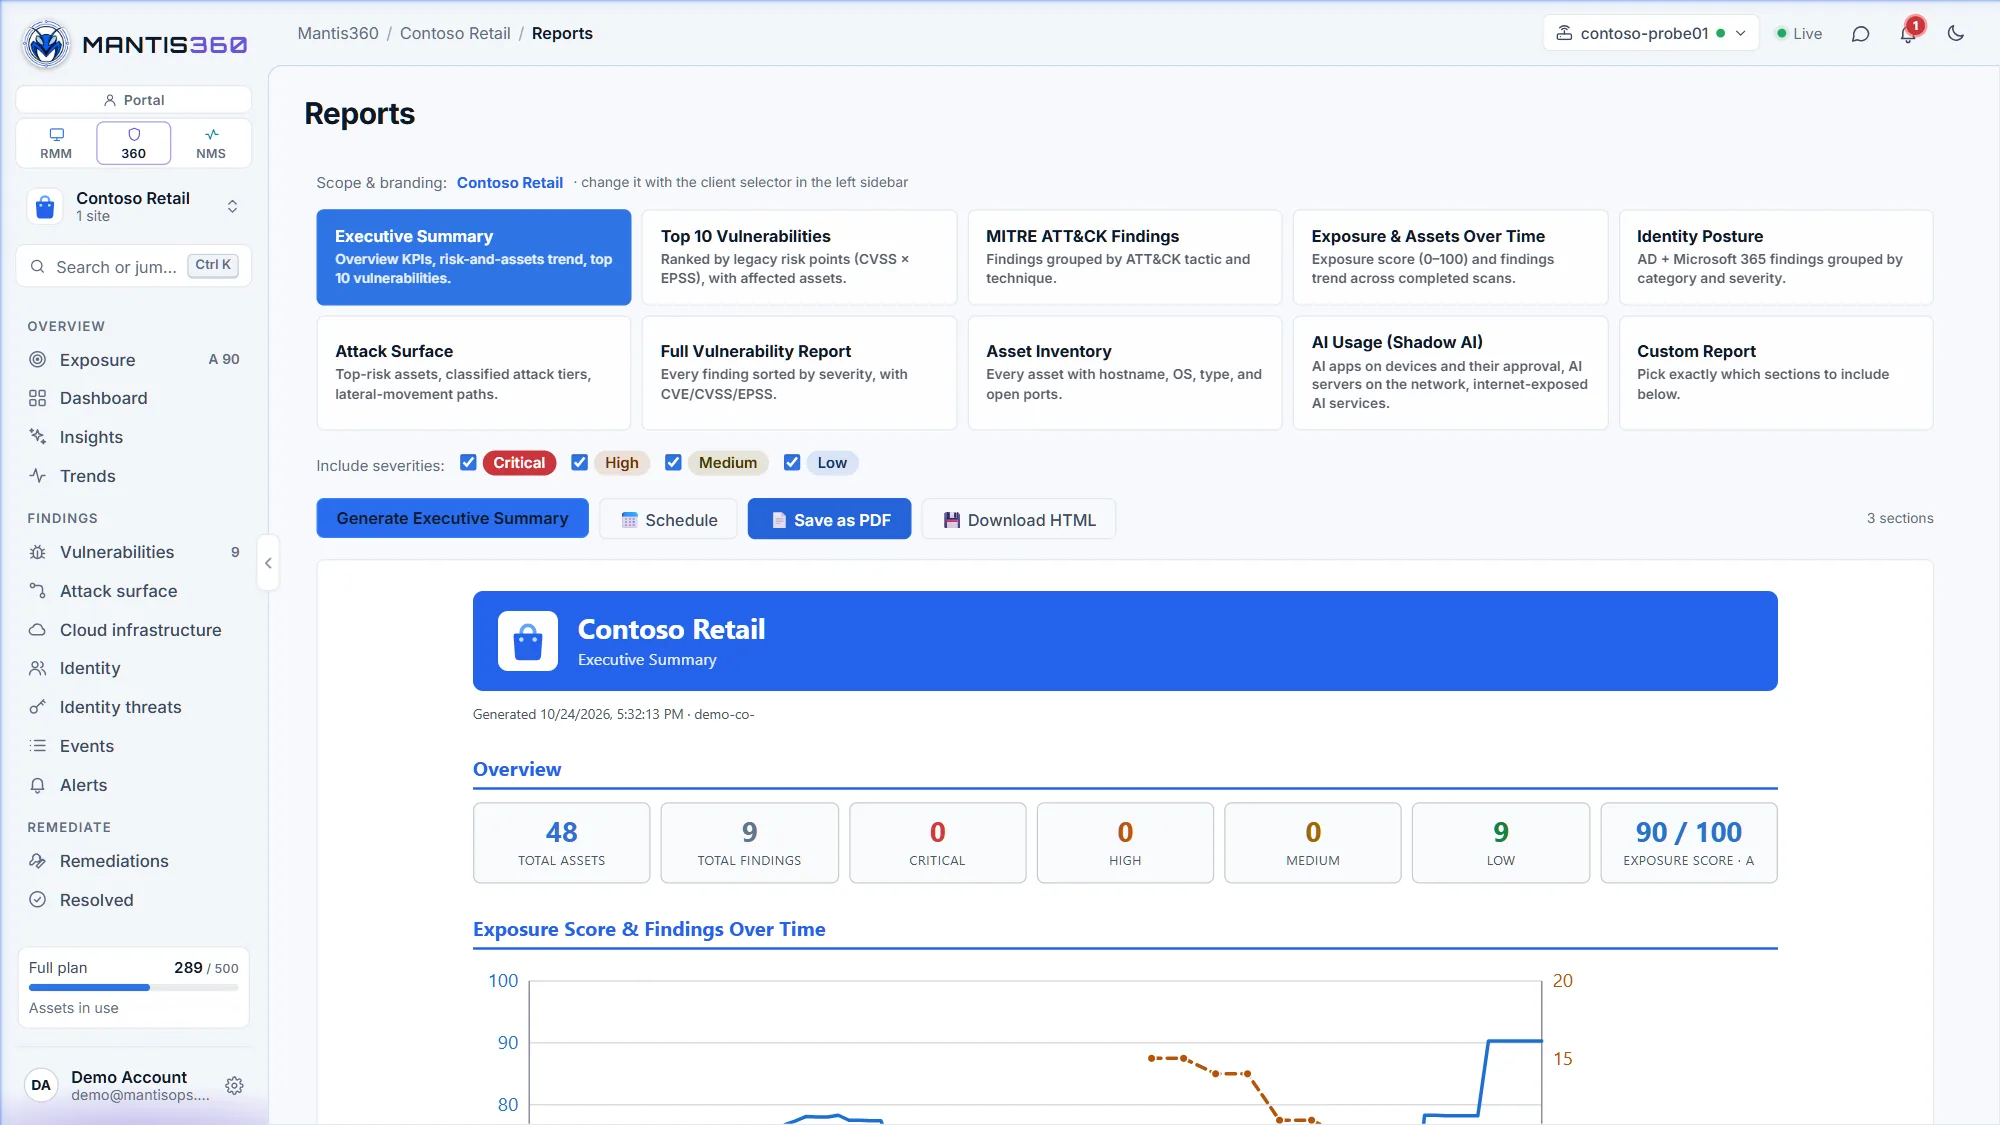
Branded reports in one click
An executive summary and nine more report types — including AI Usage — branded with your client's name and logo, saved as PDF or HTML, or scheduled.