One platform, three products. MantisRMM™ gives you full remote control over every endpoint. Mantis360™ finds, prioritizes, and auto-closes vulnerabilities the moment they're patched. MantisNMS™ watches your whole network — 50+ sensor types plus NetFlow traffic analytics — all with public, per-unit pricing and no annual contract.
Managed Automation · Network Telemetry · Intelligent Security — the three disciplines every IT team juggles, in one platform. Each maps to a product.
MantisRMM, Mantis360 and MantisNMS aren't three tools sharing a logo. They share one agent, one sign-in, one Customer Portal and one alerts inbox — and they recognise the same device in all three.
One install per device runs remote management, Mantis360 endpoint security and MantisNMS host monitoring — modules switch on with your subscriptions.
One tenant and one sign-in across all three products, with a Customer Portal that shows a combined health score and the top risks across products.
RMM alerts, NMS incidents and Mantis360 critical and known-exploited findings in one list. Acknowledge there and it applies in the product.
Each physical device appears once, matched across RMM, 360 and NMS, with gaps like a computer with no agent flagged — and one-click links into each product.
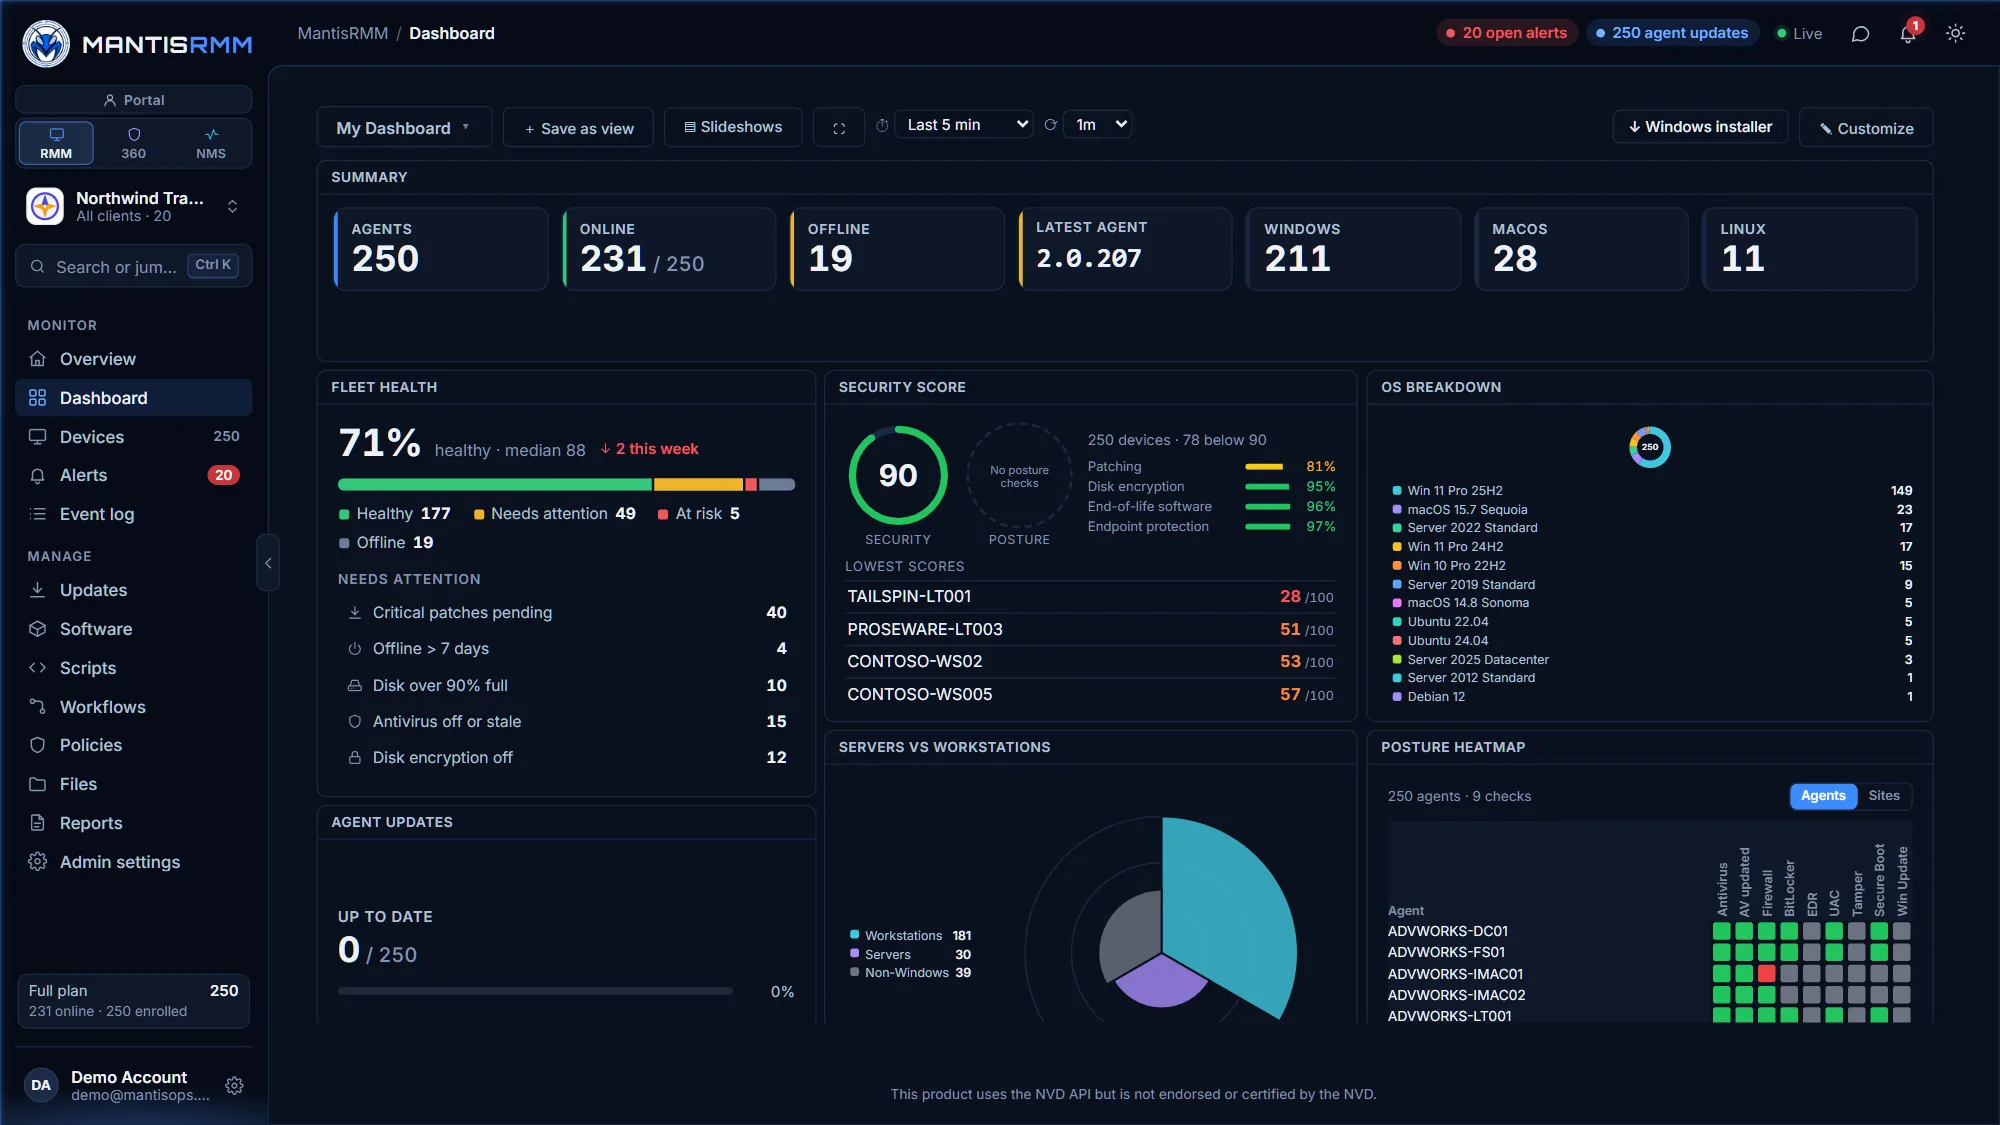
Live exposure and device-health scores, CVE tracking, and remote control across every endpoint — continuously updated as agents check in. No infrastructure to run.
Three purpose-built tools that cover remote management, vulnerability security, and network monitoring — no upsell tiers, no feature gates.
Devices sorted by health, a plain-English filter, a device page that leads with the fix, its health checklist, the same device as Mantis360 and MantisNMS see it, patching and the fleet overview.
Full remote desktop access to Windows endpoints with bidirectional clipboard sync and branded connection/disconnection notifications for the end user.
Execute PowerShell, Bash, and Python scripts across your fleet. Build workflows with chained steps, variable substitution, conditions, and Windows Update rollback.
Windows Update management, Winget software deployment, and patch status tracking across all your endpoints from a single view.
Native agents for Windows (10/11, Server), Linux (amd64 + arm64), and macOS (Intel + Apple Silicon) — all managed from one portal, with a 0–100 health score and A–F grade for every device.
Inspect running processes, kill tasks, start and stop services, browse and transfer files — all without a remote desktop session.
Software inventory auto-correlated against NVD, EPSS, and CISA KEV. See which installed software has known exploitable vulnerabilities without switching tools.
Add structured custom fields to agents and use them as dynamic variables inside scripts and automation workflows — read or write via script output.
Custom connect and disconnect toast notifications shown on the managed endpoint — keeps users informed without breaking their workflow.
Network overview and grouped incidents, the live map with device details, NetFlow talkers and conversations, the RMM agent behind a host sensor, syslog and traps, and the dashboard.
Ping (with loss & jitter), TCP/HTTP/TLS, DNS, SNMP interface & host health, SSH/FTP/NTP/LDAP/RDP, SQL Server/Oracle/MySQL/PostgreSQL, Redis, MongoDB, Redfish, VMware vCenter & Hyper-V.
NetFlow v5/v9, IPFIX, and sFlow. See top talkers, conversations, and applications per exporter — exactly which hosts and apps are using your bandwidth.
One lightweight probe monitors an entire site — no per-device agent. Or install the unified agent for CPU/mem/disk/IO/network and service, process & event-log rules straight from servers.
Threshold & syslog/trap content rules, acknowledgement, dependency-aware suppression, and notifications by email, Slack, Teams, or webhook — plus run a remediation script on the probe when a rule fires.
Auto-discovery, a live topology map of every site built from LLDP/CDP and switch tables, traceroute with a geo view, and per-interface throughput & error graphs — organize sensors into logical groups per site or company.
Store service credentials once, encrypted at rest, and reuse them across VMware, Redfish, and SSH-command sensors — secrets never leave your tenant.
A Network overview that groups related alerts into incidents with their root cause, long-term metric history tiered to your own storage, availability reports, and dashboards with per-site/company status widgets and top-port utilization.
Simple PRTG-style per-sensor tiers with no multi-year lock-in — from $175/mo for 500 sensors. Bundle with RMM & 360 for 10% off.
The exposure grade and its 90-day trend, what's holding the score down, fixes ranked by score gained, each fix's affected assets and findings, and Shadow AI usage.
200,000+ CVEs matched against your live software inventory on every agent check-in. EPSS exploit probability scoring cuts noise by up to 90%.
When software is removed from an endpoint, Mantis360 automatically closes the vulnerability finding — marked "auto-remediated" with a timestamp. No other tool does this.
Deploy a lightweight probe to any subnet and instantly discover all hosts, fingerprint services, and run vulnerability scans against network-facing devices.
Compliance scanning against CIS, DISA STIG, and custom frameworks. Track posture over time and generate audit-ready reports with remediation guidance.
Track SSL/TLS certificates and expiry across your estate and surface unexpectedly exposed services found during scans — so risky exposure is caught before it's exploited.
Active Directory posture checks — stale accounts, weak password policies, privileged group exposure, and lateral movement paths before attackers find them.
Identify industrial control systems and OT devices on your network and auto-match them against CISA ICS advisories — including fingerprinting for non-IP assets.
One 0–100 exposure score with an A–F grade for each client and your whole portfolio, the fixes that raise it most, and remediation SLAs. Findings are ranked by CVSS × EPSS, and CISA KEV findings auto-escalate to Critical.
Per-agent, per-asset, and per-sensor pricing you can calculate yourself — no quotes required, no surprise invoices, no per-technician seat fees.
When an agent confirms vulnerable software is gone, Mantis360 closes the finding on its next check-in and records it as auto-remediated — no waiting for the next scheduled scan.
Every tenant gets a dedicated D1 database and R2 object store. Your data never co-mingles with another organization's data in shared storage.
Deployed on Cloudflare's global edge. No servers to manage, no VMs to patch, no license managers. You install an agent and you're live in minutes.
Calculate your cost below. No sales call required, no annual commitment lock-in on trials. Prices exclude applicable sales tax.
Direct online purchasing opens at launch — start a free trial today.
| 500 sensors | $175/mo |
| 1,000 sensors | $325/mo |
| 2,500 sensors | $700/mo |
| 5,000 sensors | $1,250/mo |
| 10,000 sensors | $1,550/mo |
Direct online purchasing opens at launch — start a free trial today.
A quick look at how MantisOps compares to the most common alternatives. View the full feature-by-feature comparison →
| Feature | Mantis360 | Tenable | Qualys | Rapid7 |
|---|---|---|---|---|
| Findings auto-close when fixed | ✓Next check-in | ✓Next scan | ✓Next scan / agent data | ✓Next scan |
| EPSS exploit probability scoring | ✓ | ✓ | ✓ | ✓ |
| CISA KEV auto-escalation | ✓ | ✓ | ✓ | ✓ |
| ICS/OT device detection | ✓ | ✓Discovery incl.; OT Security add-on | △ | ✗ |
| Identity/AD exposure scanning | ✓ | △Separate product | △Add-on | ✗ |
| No annual contract or minimum | ✓ | ✗ | △Monthly via AWS | ✗ |
| External posture scan (A–F grade) | ✓ | △ | △ | △ |
| Security Score (KEV-weighted) | ✓ | ✓ | ✓ | ✓ |
| Free self-serve trial | ✓No credit card | ✓ | ✓ | △Trial or demo |
| Feature | MantisRMM | NinjaOne | Atera | ConnectWise RMM |
|---|---|---|---|---|
| Linux (amd64 + arm64) full support | ✓ | △ | △ | △ |
| macOS Intel + Apple Silicon | ✓ | ✓ | △ | △ |
| Branded end-user notifications | ✓ | △ | △ | △ |
| NVD CVE correlation built-in | ✓ | ✓ | △ | △ |
| Integrated VM platform | ✓Mantis360 | ✓Since 2026 | △Via Vicarius | △Security dashboard |
| Remediation scripts with rollback | ✓ | △ | △ | △ |
| LAPS — local-admin password escrow | ✓ | △ | △ | △ |
| Fleet Security Score + EOL-OS detection | ✓ | △ | △ | △ |
| Pricing | $2/agent/mo | ≤$3.75/device | $129+/tech/mo | Quote required |
| Free self-serve trial | ✓No credit card | ✓ | ✓ | ✓ |
| Feature | MantisNMS | PRTG | Auvik | SolarWinds |
|---|---|---|---|---|
| Bill only the interfaces that matter | ✓48-port switch ≈ 7 sensors | △Sensor per monitored port | ✓ | △ |
| SNMP v1 / v2c / v3 | ✓ | ✓ | ✓ | ✓ |
| NetFlow / IPFIX / sFlow analytics | ✓ | ✓ | ✓ | △Advanced tier / NTA |
| Host sensors (CPU / mem / disk) | ✓ | ✓ | △ | ✓ |
| Cloud-native SaaS (no server to run) | ✓ | △Self-hosted or Hosted Monitor | ✓ | △SaaS edition separate |
| VM + RMM in the same platform | ✓One bill, one dashboard | ✗ | ✗ | ✗ |
| No multi-year contract lock-in | ✓ | ✗3-yr term | ✓ | ✗ |
| Config backup, versioning & drift alerts (NCM) | ✓ | ✗ | ✓ | ✓ |
| VMware / Hyper-V / database / WMI sensors | ✓ | ✓ | △ | △ |
| Pricing | $175/mo · 500 sensors | ~$200/mo | Per device | From $8/node/mo |
| Free self-serve trial | ✓No credit card | ✓ | ✓ | ✓ |
Guides and references to help you deploy agents, build automations, and get the most out of each platform.
Deploy your first Windows, Linux, or macOS agent in under 5 minutes. Download the installer, run it, and your endpoint appears in the portal.
Agents are single-binary executables. Windows: MSI installer or silent install via Group Policy. Linux: shell script or systemd service. macOS: pkg installer.
Write PowerShell, Bash, or Python scripts. Use {{VARNAME}} for user variables, {{AGENT:field}} for agent fields, and {{FIELD:label}} for custom fields.
Register your organization, install 360 agents on endpoints, and your first vulnerability findings appear within minutes of the first check-in.
Deploy a network probe to any subnet. The probe binary runs continuously and reports discovered hosts, open ports, and service fingerprints to the Mantis360 portal.
Assign CIS or DISA STIG bundles to endpoints. Mantis360 scores compliance posture on every check-in and flags drifted controls with remediation steps.
Each product works independently — subscribe to MantisRMM, Mantis360, MantisNMS, or any combination. Used together as MantisOps Complete, they work as one platform: one agent, one sign-in, one Customer Portal with a single alerts inbox, and each device matched across all three products. Bundling all three saves 10%. See how the platform fits together →
Yes, free trials are available for all three products — no credit card required. Fill out the trial registration form and we'll provision your tenant. Each trial lasts 30 days with full feature access, capped at 10 devices (MantisRMM), 50 assets (Mantis360) and 100 sensors (MantisNMS), so you can evaluate everything before committing. New customers also get a 30-day money-back guarantee on their first payment.
MantisRMM is priced at $2 per agent per month, with a minimum of 10 agents ($20/month). You can add agents in increments of 10 at any time. There are no per-technician fees — all users in your organization can access the portal. An "agent" is one installed endpoint (Windows, Linux, or macOS device running the MantisRMM agent).
Mantis360 is priced at $4 per asset per month, sold in packs of 50 assets ($200/pack/month). An "asset" is any endpoint, network device, or cloud resource monitored by Mantis360 — whether through an installed agent or via network scanning. You can add packs as your asset count grows.
The MantisRMM, Mantis360, and MantisNMS host agents support:
All agents report to the same portal. No separate console or product needed per platform.
Every time a Mantis360 agent checks in (every 60 seconds by default), it reports the current software inventory. Mantis360 compares this against all open vulnerability findings for that endpoint. If the vulnerable software is no longer present, the finding is automatically marked "auto-remediated" with a timestamp and the identity of who/what removed the software. Manual remediation (where a human marks a finding resolved) creates a separate "manually remediated" audit entry. No other commercial vulnerability management tool does this automatically.
Every organization gets a dedicated D1 database and R2 object store — your data is never stored in shared tables alongside other tenants' data. Data is hosted on Cloudflare's infrastructure in the United States. MantisOps staff have admin-level access for support purposes only and do not access customer data without permission. No data is sold or shared with third parties.
Agent installation takes under 5 minutes per machine — download the installer, run it, and the endpoint appears in your portal within seconds. For network scanning, deploying a probe to a subnet takes about 10 minutes. The Mantis360 vulnerability dashboard starts populating with findings on the first agent check-in (~60 seconds after install). There are no servers, no virtual machines, and no configuration files to manage.
No. One unified MantisOps agent covers all three products: MantisRMM remote management, Mantis360 endpoint security and threat monitoring, and MantisNMS host monitoring. You install it once per device and the modules that run follow your subscriptions. In the Customer Portal each device shows up once, matched across RMM, 360 and NMS, with links straight into each product.
Shadow AI is AI people use at work without IT's approval. Mantis360 finds it in three places: AI apps on devices (matched from software inventory against a catalog of 50+ AI apps, from ChatGPT and Claude to Cursor, Otter.ai and Ollama), self-hosted AI servers on the network (from network scans), and AI services exposed to the internet without authentication (from the Security Scan, using read-only checks). Admins mark each app approved or not approved; unapproved AI becomes a finding in the exposure score and reports. Learn more →
EPSS (Exploit Prediction Scoring System) is a machine-learning model maintained by FIRST.org that predicts the probability that a given CVE will be exploited in the wild within the next 30 days. A critical-severity CVE with a low EPSS score (rare exploits in the wild) is far less urgent than a medium-severity CVE with a high EPSS score (actively exploited today). Mantis360 multiplies CVSS × EPSS to rank findings by actual risk — not just theoretical severity — which can reduce actionable vulnerability noise by up to 90%.
MANTIS is an acronym for Managed Automation, Network Telemetry, and Intelligent Security — the three disciplines the platform unifies. Managed Automation is MantisRMM (remote endpoint management and workflow automation), Network Telemetry is MantisNMS (network monitoring), and Intelligent Security is Mantis360 (risk-ranked vulnerability management). One platform, one bill, one pane of glass across all three.
The mantis is the perfect metaphor for what the platform does. It's a patient, ever-watchful predator with a near-360° field of vision — it sees everything on its turf — and the instant a threat appears it strikes with speed and precision. That's exactly how MantisOps operates: continuously watching every endpoint and network device, surfacing what actually matters, and responding fast and accurately when something's wrong. The circuit ring around the mark ties that natural instinct to the technology it protects.
Start MantisOps Complete — all three products, one agent, one portal, 10% off — or try MantisRMM, Mantis360 or MantisNMS on its own. No credit card, no infrastructure to manage.